Source: CMS OSPO Tier 2 checklist
and Tier 2 templates.
The source revision was retrieved from main for this audit. The upstream
review format is retained. Approval outcomes supplied by the project owner are
identified as reported outcomes; remaining unchecked attestations remain open.
- Already established: Git repository with a CMS-hosted remote; Python CLI, standard-library-only implementation, metric specification, engineering rules, and offline test suite. No outbound approvals were found in the inspected files.
- Missing: README, LICENSE, code.json, COMMUNITY, CONTRIBUTING, CODE_OF_CONDUCT, SECURITY, ignore rules, repolinter configuration, and all Tier 2 automation.
- Existing documentation: retain AGENTS.md and SPEC.md. SPEC.md's future snapshot milestone predates implemented snapshot support; clarify current use in README.
- Existing hygiene issue: four tracked
.pycfiles. Ignore rules cannot untrack them. No files or history will be deleted by this work. - Pre-existing working changes: tests/test_cli.py and tracked model bytecode; untracked bytecode also present. Preserve these changes.
- Unknown facts: authorized owners/contacts, project/agency/team missions, license authority, contribution and release policy, metadata classifications, supported platforms, security scope and organizational applicability.
- Human review: tier suitability, benefits/risks, independent code/security review, scan triage, licensing, full history/PII/PHI review, repository settings, and stakeholder risk acceptance cannot be inferred from source files.
- Add template-based required documents with evidence-backed technical content and searchable TODO(TIER2) placeholders for unresolved decisions.
- Add draft code.json in the current scaffolder shape; preserve unknown values rather than treating template defaults as project facts.
- Add ignore rules, resolved Tier 2 repolinter configuration, issue/PR templates, ownership placeholder, and hygiene/secret-scanning workflows.
- Validate scaffolding and re-audit. Keep all human approvals unchecked and do not publish, push, change visibility, remove files, or rewrite history.
- repolinter.json is the recursively merged tier0 → tier1 → tier2 configuration
at the pinned source revision, preserving all upstream rule levels. This avoids
unresolved
extendswith the standalone repolinter CLI. It checks file/section presence, not factual completeness or approval. It does not validate code.json. - repoHygieneCheck.yml runs those local rules on pushes, PRs, and manual dispatch. The upstream first-run labels, configuration overwrite, and PR-writing/PAT machinery are omitted; validation needs only read permissions and no external publication. No check is weakened.
- Gitleaks workflow and custom rules are copied from Tier 2. They are not a full vulnerability/privacy assessment, and the custom patterns have limited scope.
- CODEOWNERS uses GitHub's recognized filename instead of upstream CODEOWNERS.md.
- LICENSE now contains the approved CC0 1.0 Universal text. The project owner
reports approval by
decause-govon 2026-10-13 and confirms the terms apply to outside contributions. - code.json contains project-owner answers and retains TODO values only for
public fork/clone counts that cannot be observed before publication. The
contract number is recorded as
[0]per the owner's instruction; CMS schema acceptance of an integer array item must still be verified. - The target repository and website are future destinations. Public GitHub settings, hosted workflow runs, SBOM availability, and reuse counts must be verified after the switch. Administrators will enable Dependabot alerts, secret scanning, and branch protection after the switch.
- Optional
contributors.yml, auto-changelog, and updateCodeJSON automations remain omitted. DCO is not required. There are no tracked.pycfiles in the current Git index; the initial audit's four-file finding is historical. - Branch/merge workflow, release policy, and recurring code-scan schedule and
responsible role are deferred. Static code vulnerability analysis remains
pending.
SECURITY.mdremains unchanged at the project owner's direction. - The project owner reports a one-reviewer waiver, completed full-history review, and stakeholder outcomes as documented in the sections below. Public release, communications, and inventory tracking remain future actions.
Validation performed on 2026-10-07:
npx --yes --cache /tmp/libyears-tier2-npm-cache repolinter@0.12.0 lint .: exit 0; all required checks passed. Nine optional warnings remain: README branching model, governance, glossary; CONTRIBUTING team-specific guidelines; COMMUNITY maintainer, approver, reviewer, contributor, and alumni lists. Linguist and Licensee axioms could not run because those tools are absent. License text/authority and placeholder content have not been validated by this pass.gitleaks git . --config .github/.gitleaks.toml --redact --no-banner --report-format json --report-path /tmp/libyears-tier2-gitleaks.json: Gitleaks 8.30.1 exited 0; 11 local commits scanned with no findings under the six Tier 2 custom patterns plus Gitleaks built-in rules (enabled withextend.useDefault). A synthetic GitHub fine-grained token canary was detected by built-in rulegithub-fine-grained-pat; that canary was outside the repository. This is limited automated evidence, not a full privacy, credential-management, or commit-history review. Uncommitted files are outside this history scan. The redacted report is temporary, not a repository artifact.- Python standard-library validation: both JSON files parse; code.json retains all upstream top-level fields; all 63 resolved repolinter rules and their levels match the upstream inheritance chain. Local Markdown links resolve, template expressions are rendered, and human checklist attestations remain unchecked.
- Node
js-yamlparsing (from repolinter's temporary installation): both workflows parse, contain triggers/jobs, and use read-only contents permissions. Hosted Actions have not run; parsing is not execution validation. git diff --check: passed. Existing user changes were preserved.- Application tests were not run: this authorization requested repository artifact validation. The local Python is 3.11, which meets the current 3.11+ minimum; CONTRIBUTING.md's older 3.12+ minimum is corrected in this update.
- CMS code.json validation used the current
DSACMS/gov-codejsonCMS schemaschemas/cms/schema-2.1.0.jsonwith Ajv 8.20.0, Draft 2020-12, and ajv-formats 3.0.1. Overall validation fails on the known TODO placeholders in status, license, usageType, organization, repositoryURL, visibility, laborHours, reuseFrequency, platforms, maintenance, contact email, feedbackMechanism, FISMA, subsetInHealthcare, and userType. The unresolved public repository URL specifically failsformat: uri;privatealso fails this validator despite explanatory prose in the metadata docs. No fictitious URL was supplied. Dates record root commit creation and metadata edit, not release or approval dates.
Re-audit against the full checklist:
| Requirement area | Repository preparation result | Outbound review status |
|---|---|---|
| Prerequisites | Tier 2 suitability approval reported by project owner | Hosting access and outbound switch remain external actions |
| Benefits and risks; sensitive-data questions | Project-owner answers recorded; six selected benefits marked | Outcomes are reported by project owner, not independently verified |
| Independent code review | One review and a one-reviewer waiver reported | Review evidence is not included in this repository |
| Code analysis | Gitleaks no-findings result reported | Static code analysis pending; schedule and responsible role deferred |
| Licensing | CC0 1.0 approval and outside-contribution terms reported; license text added | Review evidence is not included in this repository |
| Commit history | Full-history review and Gitleaks no-findings results reported | Review evidence is not included in this repository |
| Repository hygiene | Owner/maintainer, policies, AI policy, and community information recorded | JSON/YAML, local Markdown links, and diff checks passed; repolinter could not run because npm registry DNS was unavailable and its package was not cached |
| Project metadata | Supplied values recorded; future repo URL and SBOM path supplied | Fork/clone counts and CMS schema acceptance of contractNumber: [0] remain unresolved |
| Repository details | Description, website, and topics supplied | Admin configuration and hosted availability remain external actions |
| Risk acceptance | Sign-offs and not-required decisions reported by project owner | No independent sign-off artifact is included in this repository |
| Public release and rollout | No outbound action taken | Hosted settings, publication, communications, and inventory tracking remain |
The repository is prepared for further review, not cleared for outbound release. File and heading presence do not satisfy unresolved substantive requirements.
The project owner supplied the project facts, policy choices, review outcomes, waiver, and sign-offs recorded in this checklist. Reported reviews and approvals are attributed to the named reviewer and date; their source artifacts are not included here. Repository files were updated only after the project owner authorized the write step.
This is a review process to approve CMS-developed software to be released open source at github.cms.gov. If you would like your repository to be released, please complete the following steps.
State the Benefits of Open Sourcing the Project
State the Risks of Open Sourcing the Project
Sign off on risk acceptance of open-sourcing the software product
Flipping the Switch: Making the Repository Public
Your project should be stored in a GitHub repository If you are new to GitHub or repositories, checkout the OSPO's Beginner Guide to Creating GitHub Repos before moving on to the next steps.
Does your repository align with the requirements of a Tier 2 project? To verify:
- Review the flowchart or use
tier-determiner.pyprovided in the README.md. - Read more about Tier 2 and the overall CMS OSPO maturity model framework.
Tier 2 suitability was approved by decause-gov on 2026-10-13, as reported by
the project owner. The intended destination is https://github.com/DSACMS/libyears;
it remains a future public destination until the outbound switch is completed.
-
Cost Savings
By making the project freely available, this reduces licensing and acquisition costs.
-
Ease of Repurposing
The open nature of the code allows users to modify and adapt the software to suit their specific needs, fostering customization and flexibility.
-
Minimization of Vendor Lock-in/Flexibility of Vendor Choice
Users are not tied to a single vendor, providing the freedom to choose between different vendors.
-
Enable Transparency
The source code is accessible and visible to anyone, promoting transparency in how the software functions, which helps build trust.
-
Enable extension/extensibility
Users can extend and enhance the functionality of the software by adding their own features.
-
Increase Interoperability
Planning in the open enables future compatibility and interoperability between different systems and software applications.
-
Facilitate Experimentation/Early Adoption
Working in the open encourages experimentation and early adoption of cutting-edge technologies, leading to faster innovation and improvement in software capabilities.
The project owner reports no ongoing costs and no connection to CMS-internal systems, no private PII/PHI or privacy risk, no CMS credentials, and no job-code requirement. These are project-owner responses, not independent findings.
-
Security Risks
Vulnerabilities may be exposed if the code is not thoroughly reviewed, potentially leading to security breaches or exploitation. (See: SECURITY.md) Does this project connect to any CMS-internal only systems? Does this project require authorization or authentication to operate? Does this project detail any non-public directories of CMS/HHS systems or people?
-
Financial Risks
Costs may arise from maintaining code, community engagement, addressing security concerns, subscription costs, hardware costs, specialized tooling or infrastructure costs among others. Does this project require any ongoing financial costs or subscription fees? (e.g., Cloud Hosting, Specialized build systems, paid maintainers, paid libraries or dependencies.)
-
Privacy Risks
Does this project require access to non-public, non-synthetic PII, PHI, or other internal-only CMS systems containing such data or information?
-
Does the code contain or touch any private information such as Personal Identifiable Information (PII) or Protected Health Information (PHI)?
- What PII or PHI does this project contain?
-
Does the code interface with any of CMS’ internal-only systems (e.g. mainframes, JIRA instances, databases, etc…)?
- What processes do you go through internally to get access to the systems?
-
Does the repository contain any keys or credentials to access or authenticate with CMS’ systems?
-
Does this repository require any job codes to run?
If you answered “yes” to any of the above questions, your project may be ‘sensitive’ in nature and require a more thorough review before sharing publicly. Please reach out to opensource@cms.hhs.gov for guidance. If you answer yes to any of these questions above, it is best to NOT open source the product due to security reasons.
The project owner reports the risk answers above and the related stakeholder
sign-offs by decause-gov on 2026-10-08. The project owner reports the required
security/privacy, national-security/intelligence, FOIA, export, TSA, and
classified-information attestations were covered in that sign-off.
The existing codebase should be given a one time, top-to-bottom code quality and security vulnerability review by two (or more) engineers who have written production code within the past two years, in the languages used in the project. Engineers should review credential management practices with the development team to ensure that any keys, passwords, or other sensitive configurations are not checked into source code or in the git history.
The engineers can be federal government employees or trusted partners from outside the agency from other contracts, or from independent testing contracts. Their names, organizations, comments and approval/disapproval on the overall codebase should be tracked in this document.
To provide independent review, the engineers should not have been involved in the development of the software product. This includes engineers who wrote part of the software or who directly provided technical direction and oversight in the creation of the software.
As part of the code review, engineers should reference modern listings of the most significant software security vulnerabilities. For instance, an acceptable description would be that the engineers showed how they used automated tools and manual review to check each item in OWASP's current 10 Most Critical Web Application Security Risks.
One code review was completed by decause-gov on 2026-10-08, following the
CMS OSPO Tier 2 outbound review checklist, as reported by the project owner.
The project owner reports an authorized waiver of the two-reviewer requirement
by decause-gov on 2026-10-08. This record reflects the reported waiver; the
underlying review artifact was not added here.
At least one automated tool for code analysis (such as static code analysis tools) has been run on the codebase to look for security vulnerabilities, and results have been appropriately acted upon. Even if all findings are eventually fixed, if the initial scans revealed significant, severe vulnerabilities (such as SQL injection vulnerabilities), this indicates that the software development team may not be adhering to the best practices required for open source public release.
Automated tooling for code analysis should be incorporated as a regularly scheduled part of the application development process. The development team should briefly document how frequently they commit to running these automated scanning tools, and who will be running the tests, interpreting, and acting upon the results.
Below is a list of suggested tools to run for code analysis:
| Tool | Description | Link |
|---|---|---|
| Repo Linter | Lint repositories for common issues such as missing files,etc... | https://github.com/todogroup/repolinter |
| Gitleaks | Protect and discover secrets using Gitleaks 🔑 | https://github.com/gitleaks/gitleaks Use and run gitleaks.yml provided in repository |
| git filter-repo | Entirely remove unwanted files / files with sensitive data from a repository's history | https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/removing-sensitive-data-from-a-repository |
| bulk_extractor | Check for secrets, URLs, emails, etc. | bulk_extractor Official Documentation OSPO Guide Documentation |
Gitleaks was run on 2026-10-08 with no findings, as reported by the project owner. Gitleaks checks for secrets and does not complete the required static code vulnerability analysis. That analysis remains pending. Scan frequency and responsible role are deferred.
Ensure that acceptable licensing is decided for the project. Most often, software released as open source by the federal government does so under the Creative Commons Zero 1.0 license.
Suggested licensing:
Public Domain
This project is in the public domain within the United States, and copyright and related rights in the work worldwide are waived through the CC0 1.0 Universal public domain dedication.
All contributions to this project will be released under the CC0 dedication. By submitting a pull request, you are agreeing to comply with this waiver of copyright interest.
If your project is not being dedicated to the public domain under CC0, due to being work for hire, or some other documented reason, then choosing another OSI approved license is the next best thing.
CC0 1.0 Universal was approved by decause-gov on 2026-10-13, as reported by
the project owner. The project owner confirmed the same CC0 terms apply to
outside contributions. The approved license text is in LICENSE.
Review the history of commits to the version control system used, and whether the team prefers to clean (e.g., rebase) this history before releasing to the public.
If not rebasing, verify that:
- There are no obscene or impolite remarks in comments or commit history
- There are no sensitive internal URLs/IP Addresses in comments or commit history
- There are no credential files such as Passwords, API/SSH/GPG keys checked into the repo.
Consider using the following tools to perform the tasks above:
| Tool | Description | Link |
|---|---|---|
| gitleaks | Open source tool that detects and prevents secrets (passwords/api/ssh keys) checked-in to your git repo | https://github.com/gitleaks/gitleaks What is git leaks and how to use it? Use and run gitleaks.yml provided in repository |
| git filter-repo | Entirely remove unwanted files / files with sensitive data from a repository's history | https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/removing-sensitive-data-from-a-repository |
| bulk_extractor | Check for secrets, URLs, emails, etc. | bulk_extractor Official Documentation OSPO Guide Documentation |
The project owner reports that decause-gov completed a full-history review on
2026-10-08 with no findings. Gitleaks was also reported to have no findings on
2026-10-08. These reported outcomes cover the review and scan; they do not
independently verify their scope or evidence.
As part of our repository hygiene requirements, the project must include certain files and sections. Using repolinter will help you identify missing files and content that will need to be added to your repository before outbounding.
- Install repolinter
npm install -g repolinter
-
Add repolinter.json to the root directory of your project
-
Run command:
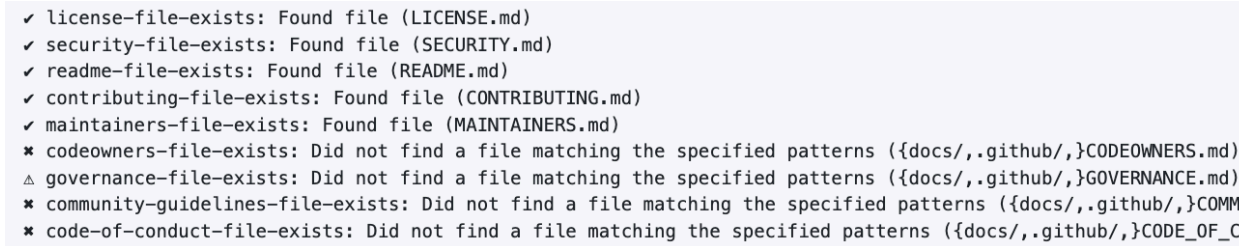
repolinter lint .
- The result produces a list of files section existence checks, indicating whether each requirement was met or not.
-
Add the tier-specific repoHygieneCheck.yml to the github directory of your project. The file includes a job that runs repolinter called repolinter-checks
-
Manually trigger the workflow.
-
The result produces an issue on the repository with a list of file and section existence checks, indicating whether each requirement was met or not.
The project should include the following files and sections (link to templates):
-
LICENSE
License of your project, whether public domain (CC0) or other OSI-approved License. Using ‘vanilla’ license text will allow for GitHub to auto-label the license information on the repository landing page.
-
code.json
Contains metadata about the project, refer to Review Project Metadata
-
README.md
An essential guide that gives viewers a detailed description of your project
| Section | Description | Included? |
|---|---|---|
| Project Description | This should be 1-3 sentence short description of the project that can be used as a 'one-liner' to describe the repo. A best practice is using this same language as the official 'description' on a GitHub repo landing page. | ✅ ❌ |
| About the Project | This should be a longer-form description of the project. It can include history, background, details, problem statements, links to design documents or other supporting materials, or any other information/context that a user or contributor might be interested in. | |
| Project Vision | This should be a forward-looking statement that outlines the desired future state or long-term goals of the project. | |
| Project Mission | This should be a statement that defines the purpose, scope, and specific objectives of the project. | |
| Agency Mission | Agency-led projects should include information about their agency mission. This should be taken directly from agency websites or wikis. | |
| Team Mission | Agency-led projects should include information about the team executing on the mission. This should be taken directly from internal team charters and functional statements. | |
| Core Team | This information helps with succession planning and provenance for security compliance and remediation. It helps future users and contributors understand where the code originated. | |
| Local Development | Use step by step instructions to get from 'zero' to 'running code.' | |
| Coding Style and Linters | Best practices contributors should follow to reduce friction and improve readability, functionality, and quality of contributions. | |
| Contributing | For projects that accept contributions, point towards the CONTRIBUTING.md file. | |
| Community | Point your contributors towards wherever your community exists (e.g. email lists, online discussion boards or channels, project backlogs and documentation, etc.). | |
| Community Guidelines | This section points to a CODE_OF_CONDUCT.md file or website providing information around acceptable conduct and reporting mechanisms and escalation strategies. It is better to have these processes defined before they are needed, so you can focus on support if/when there is an incident (e.g. Contributor-covenant.org). | |
| Policies | This section is to explicitly link to Federal policies and guidelines that are required or recommended for Federal projects to comply with, such as Accessibility (508), Interoperability, Anti-deficiency, Security, Licensing, and other policies that can vary between agencies and domains. | |
| Public Domain | A best practice is to list the LICENSE under which a project is released at the bottom of the README. In most cases for Federal repos, we default to Creative Commons Zero 1.0 International (world-wide public domain). |
-
COMMUNITY.md
Outlines the community members, roles, responsibilities, and guidelines for participating in the project.
| Section | Description | Included |
|---|---|---|
| Table of Project Members | Who are the points of contact in your project who are responsible/accountable for the project? This can often be an engineering or design manager or leader, who may or may not be the primary maintainers of the project. | ✅ ❌ |
| Principles | This section communicates to prospective contributors and users what the values of your community are. The examples provided in the template were established by the Justice40 project at USDS. | |
| Community Guidelines | This section communicates specific norms and guidelines for how to participate and contribute positively to your community. The more explicit you can be about behaviors you'd like to encourage or discourage, the less friction new contributors will experience in onboarding and operating within your project. | |
| Acknowledgements | This section recognizes previous work and best practices established by the other members of the federal open source community such as USDS, GSA, 18F, and the Justice40 Project. |
-
CONTRIBUTING.md
Provides guidance on how users can run your project and make contributions to it
| Section | Description | Included |
|---|---|---|
| How to Contribute | Basic instructions about where to send patches, check out source code, and get development support. | ✅ ❌ |
| Getting Started | Includes installation steps, prerequisites for installation, and instructions for working with the source code. | |
| Building dependencies | This step is often skipped, so don't forget to include the steps needed to install on your platform. If your project can be multi-platform, this is an excellent place for first time contributors to send patches. | |
| Building the Project | Be sure to include build scripts and instructions, not just the source code itself! | |
| Workflow and Branching | If your project has a preferred workflow or branching structure, mention it here. We recommend 'git flow' as a good default. | |
| Coding Style and Linters | HIGHLY ENCOURAGED. Specific tools will vary between different languages/frameworks (e.g. Black for Python, eslint for JavaScript, etc.). | |
| Writing Issues | Make a brief statement about where to file issues, and conventions for doing so. Link to ISSUE_TEMPLATE.md file. | |
| AI Usage | Define how AI can be used in your project with recommended and non-recommended uses. Link to PULL_REQUEST_TEMPLATE.md which includes a section for contributors to disclose AI usage | |
| Policies | This section is here to explicitly link to Federal policies and guidelines that are required or recommended for Federal projects to comply with, such as Accessibility (508), Interoperability, Anti-deficiency, Security, Licensing, and other policies that can vary between agencies and domains. | |
| Public Domain | This section is to explicitly link to Federal policies and guidelines that are required or recommended for Federal projects to comply with, such as Accessibility (508), Interoperability, Anti-deficiency, Security, Licensing, and other policies that can vary between agencies and domains. |
-
SECURITY.md
Details security policies and procedures
-
CODE_OF_CONDUCT.md
Defines the code of conduct for contributors
-
repolinter.json
Lints repository for missing files and sections above
As you are writing content about the repository, consider the following when describing the project, the agency, and how work is done:
- Focus on solutions, not problems Rather than describing the negatives and shortcomings of an existing project, process, or group, focus on highlighting the benefits, outcomes, and positive impacts of the solution. Be constructive and accentuate the positive.
- Use Plain Language Be clear and concise when explaining concepts. Avoid jargon unless it is necessary and well-defined. Use active voice to be clearer and more engaging.
- Focus on the audience Write for a broad audience, ensuring that developers, stakeholders, end-users, and viewers of all skill levels can understand and engage with the content.
Please refer to the style guides below for additional tips and guidance:
- CMS Resources
- 18F Style Guide
- UK Content Style Guide
Local repository artifacts and policy text have been updated from the answers
and evidence recorded in this session. Four .pyc files were reported in the
initial audit; the current Git index contains no tracked .pyc files. JSON
parsing passed for code.json and repolinter.json; all three workflow YAML
files parsed; local Markdown links passed in six reviewed documents; and
git diff --check passed. Repolinter could not run: npm registry DNS resolution
failed in the sandbox, and the requested package was not in the local npm cache.
The CMS code.json schema was not available for validation; contract-number
acceptance and pre-publication fork/clone values remain unresolved.
As part of the SHARE IT Act, Federal Source Code Policy, and the agency’s software inventory tracking initiatives, each repository must contain a code.json file, storing metadata on your project.
For more information on code.json, please review the gov-codejson documentation repository.
Using form site
Users can fill out a web form that creates a code.json file to be uploaded to a project's source code repository: https://dsacms.github.io/codejson-generator.
Using automated-codejson-generator
The automated-codejson-generator is a GitHub Action that automatically generates and maintains code.json files for federal open source repositories. It ensures schema consistency and automates various metadata calculations.
**Using the repo-scaffolder cookiecutter CLI (upstream alternative)
The cookiecutter generation directory is not installed in this existing repository. The following upstream procedure requires a separate scaffolder checkout; do not run its repository-creation hooks here. This repository already has a draft code.json.**
- Install cookiecutter
python3 -m pip install --user cookiecutter
- In the
.githubdirectory, run the command:
cookiecutter . –directory=codejson
-
Answer various questions about your project.
-
A code.json file will be generated with your responses.
As you continue development in this repository, it is important to keep this file up-to-date. Our automated-codejson-generator can assist with updating this file.
Known fields are populated from project-owner answers. Public reuse counts are
not available until publication. The intended repository URL and visibility
describe the future public destination. CMS schema validation must confirm the
contract number array containing integer 0; the owner specified this value.
The project owner reports FISMA Low classification reviewed by decause-gov on
2026-10-13. The intended supported platforms are Linux, macOS, and Windows;
Windows support is included in the CI matrix.
The GitHub repository homepage features a concise description of the project, a list of relevant topic tags, and general information about the repository to provide a comprehensive overview for users and contributors.
About Section:
-
Description
1-2 sentences describing the project
-
Website
Link to project’s website
-
Topics
Tags for project discoverability. Helpful topics to classify a repository include the repository's intended purpose, subject area, community, or language.
Include in Home Page:
- Releases
- Packages
- Deployments
The project owner approved the description, website https://dsacms.github.io/libyears,
and topics python, pypi, libyears, dependency-freshness, and npm.
Repository administrators will configure the About details after the public
switch. Releases, packages, and deployments are not yet available to verify.
See the local audit and remediation notes at the beginning of this file.
- Date: 2026-10-08 (reported by project owner)
- Repository Name: Libyears
The project owner reports that decause-gov signed off on the business-owner
risk acceptance and the security/privacy and regulatory attestations on
2026-10-08. The project owner also reports ISSO and ISG sign-offs as not
required, recorded by decause-gov on 2026-10-08. This approval record is based
on the project owner's report; the signed source artifact is not attached.
Before outbounding this repository, it’s important that the appropriate stakeholders review and acknowledge the risks and responsibilities associated with releasing the code to the public. This step ensures transparency and accountability while enabling informed decision making.
- I acknowledge that this project does NOT:
- contain any PII/PHI, or create an identifiable risk to the privacy of an individual.
- interface with any CMS Internal Systems.
- contain any keys or credentials to authenticate with CMS systems.
- I acknowledge that this project is NOT:
- primarily for use in national security systems, as defined in Section 11103 of title 40, USC.
- created by an agency or part of an agency that is an element of the intelligence community, as defined in section 3(4) of the National Security Act of 1947.
- exempt under section 552(b) of title 5, USC (commonly known as the "Freedom of Information Act").
- I acknowledge that this project is NOT prohibited under:
- Export Administration Regulations.
- International Traffic in Arms Regulations (ITAR).
- Regulations of the Transportation Security Administration related to the protection of sensitive information.
- Federal laws and regulations governing the sharing of classified information.
If all boxes have been checked, please proceed to the Flipping the Switch section below this one, otherwise, this section must be filled out and approved by the indicated stakeholders before public release.
After reviewing the materials prepared by the team that is working to open source the product, the business owner signs off on a risk acceptance for open-sourcing the software product.
Requesting sign off from key people on this request.
| Reviewer Organization | Reviewer Names | Reviewer’s Recommendation |
|---|---|---|
| Code Reviewer Recommendation | decause-gov |
Approved 2026-10-08; one-reviewer waiver reported, authorized by decause-gov on 2026-10-08 |
| ISSO | decause-gov |
Not required; signed off 2026-10-08 |
| ISG Technical Approval | decause-gov |
Not required; signed off 2026-10-08 |
| Business Owner(s) | CMS OSPO / decause-gov |
Risk acceptance signed off 2026-10-08 |
Once the repository has passed outbound review, we are ready to “flip the switch” and officially make it public. Once made public, there are a couple of actions that need to be taken:
The repository is a future public destination. Repository administrators will enable Dependabot alerts, secret scanning, and branch protection after the switch. GitHub Actions and hosted workflow execution will also be enabled and verified after the switch.
Please enable the following features to enhance repository security and maintain code quality:
-
Dependabot Alerts
A GitHub Feature. Get notified when one of your dependencies has a vulnerability
-
Secret Scanning Alerts
A GitHub Feature. Get notified when a secret is pushed to this repository. Ideally set this up to run after each new commit is pushed to the Repository.
-
Branch Protections
Ensures the integrity of important branches by preventing unauthorized actions like force pushes and requiring pull request reviews with specific checks before merging. Dev and main should be protected branches in the repository.
-
Git Branching
After making the repository public, make sure there is a coherent git branching plan in place. For example: agree to merge feature related pull requests into dev but merge bug fixes into main instead of dev first.
-
Add Repolinter GH Action to CI
For ongoing adherence to repository hygiene standards, integrate the repolinter GitHub Action into your CI pipeline. This addition enhances your workflow by automatically enforcing repository cleanliness standards.
-
Optional: DCO (Developer Certificate of Origin)
Project policy: DCO sign-off is not required.
Requires all commit messages to contain the Signed-off-by line with an email address that matches the commit author. The Developer Certificate of Origin (DCO) is a lightweight way for contributors to certify that they wrote or otherwise have the right to submit the code they are contributing to the project. The GitHub app to enforce DCO can be found here .
Share the good news with communities both inside and outside CMS!
-
Draft a launch announcement Be sure to include the following information:
-
Repo Description
- Repo URL
- Authoring Team Email Contact
- Authoring Team URL
- Authoring Team Slack Channel
- Call to action (File issues, contribute PRs)
-
Post launch announcement to CMS slack channel
- #cms-opensource
- #cms-api-community
- #cms-data-community
- #cms-engineering-community
- #ai-community
-
Send a launch announcement email
-
Add launch announcement to a Confluence Wiki Page
Add your project to our inventories via code.json.
- Add a completed code.json file to the repository